HefestoAI checks AI-generated code before it merges. One run gives you a terminal report, a SARIF file for GitHub code scanning, and a CI gate that exits 1 on HIGH findings or worse.
The Problem
Linters validate syntax. Test suites validate implementations. Neither validates intent.
AI-generated code looks clean. It compiles. It passes tests. But it quietly breaks business logic — charging users daily instead of monthly, inverting permission checks, corrupting data at scale.
That's semantic drift. And traditional tools can't catch it.
How It Works
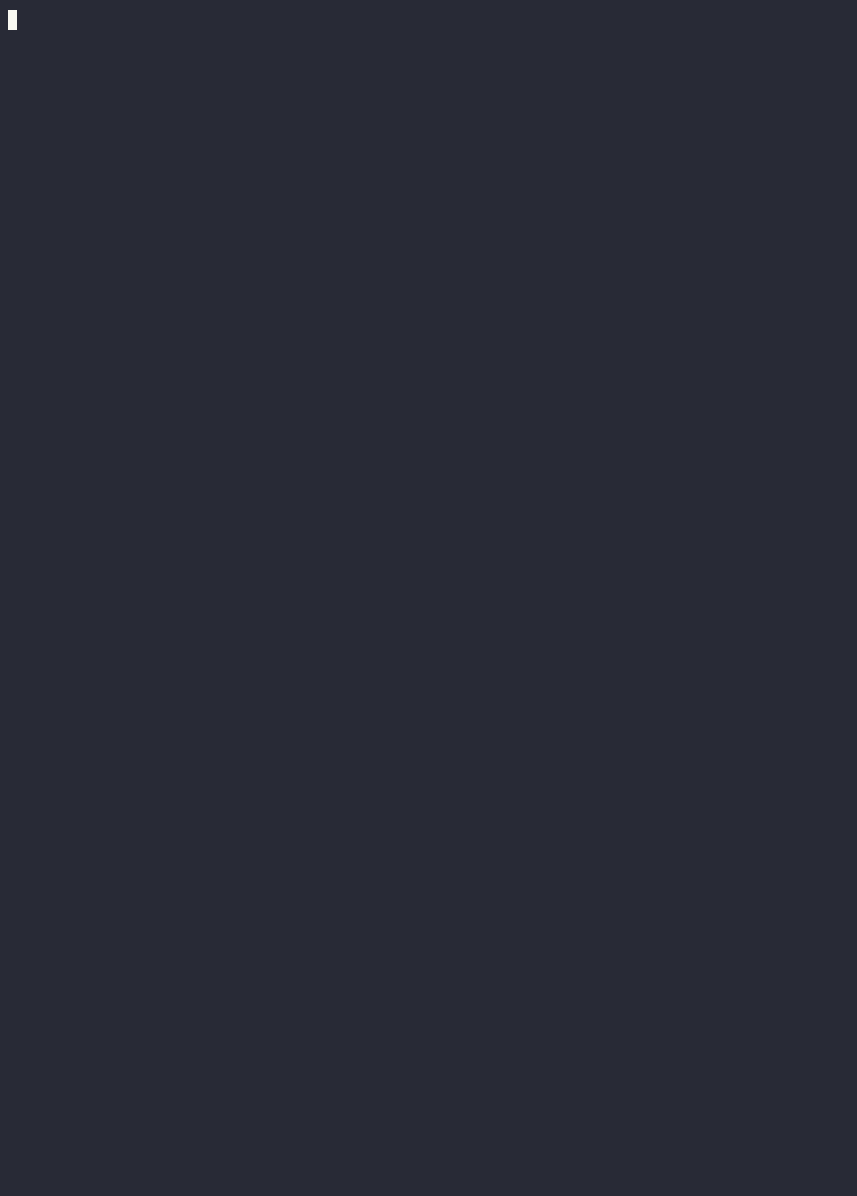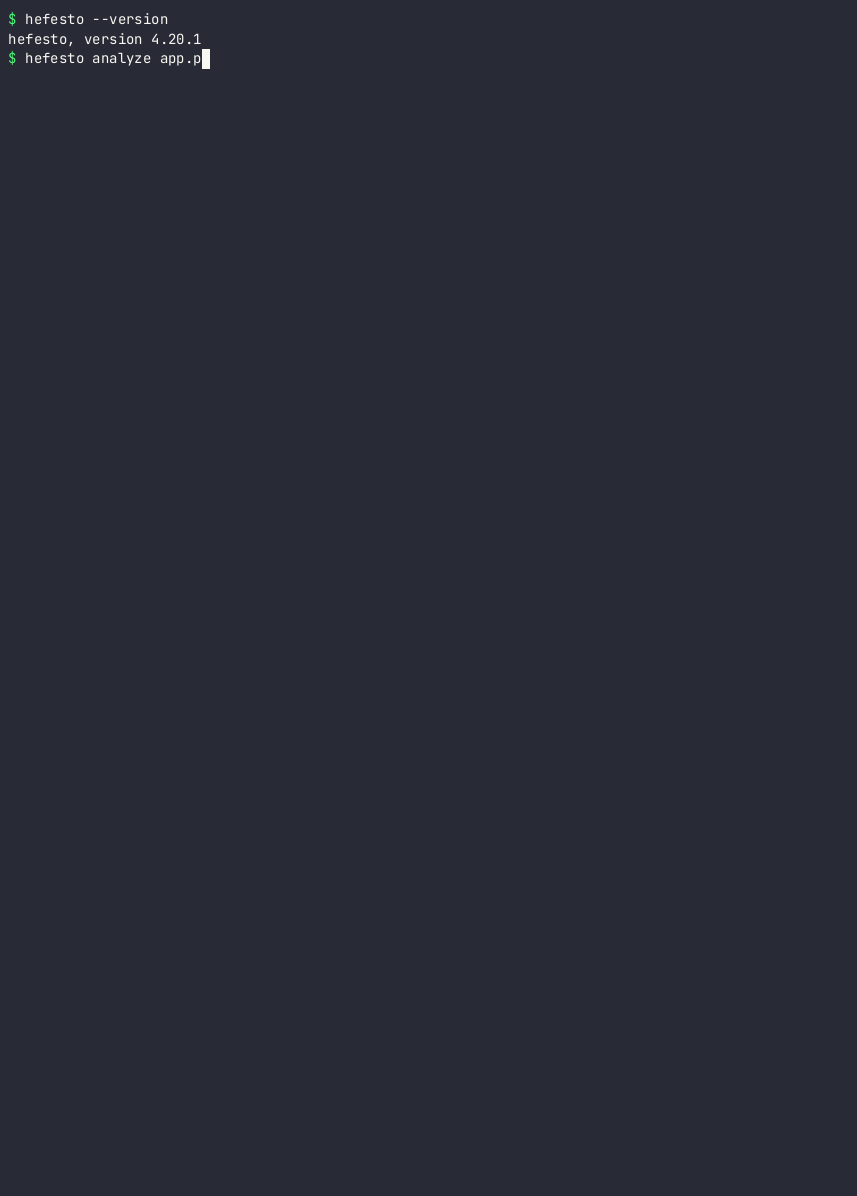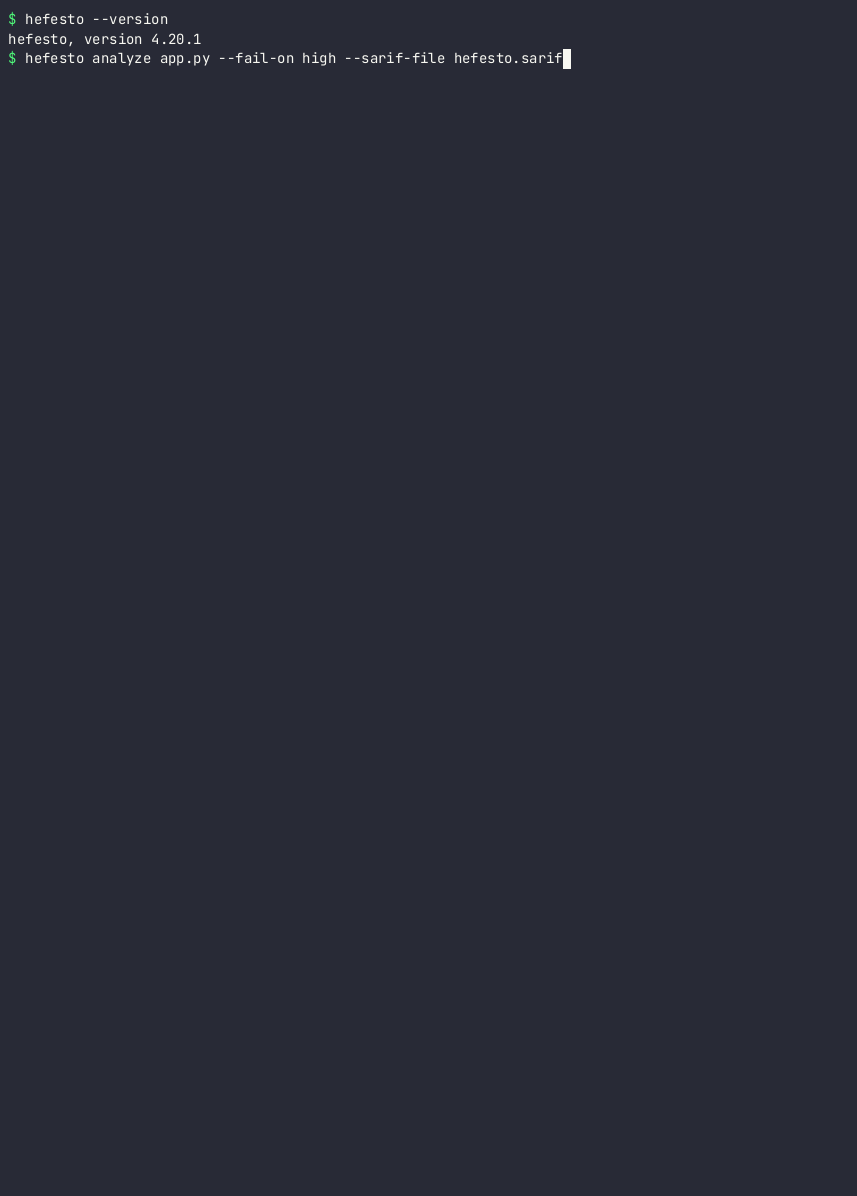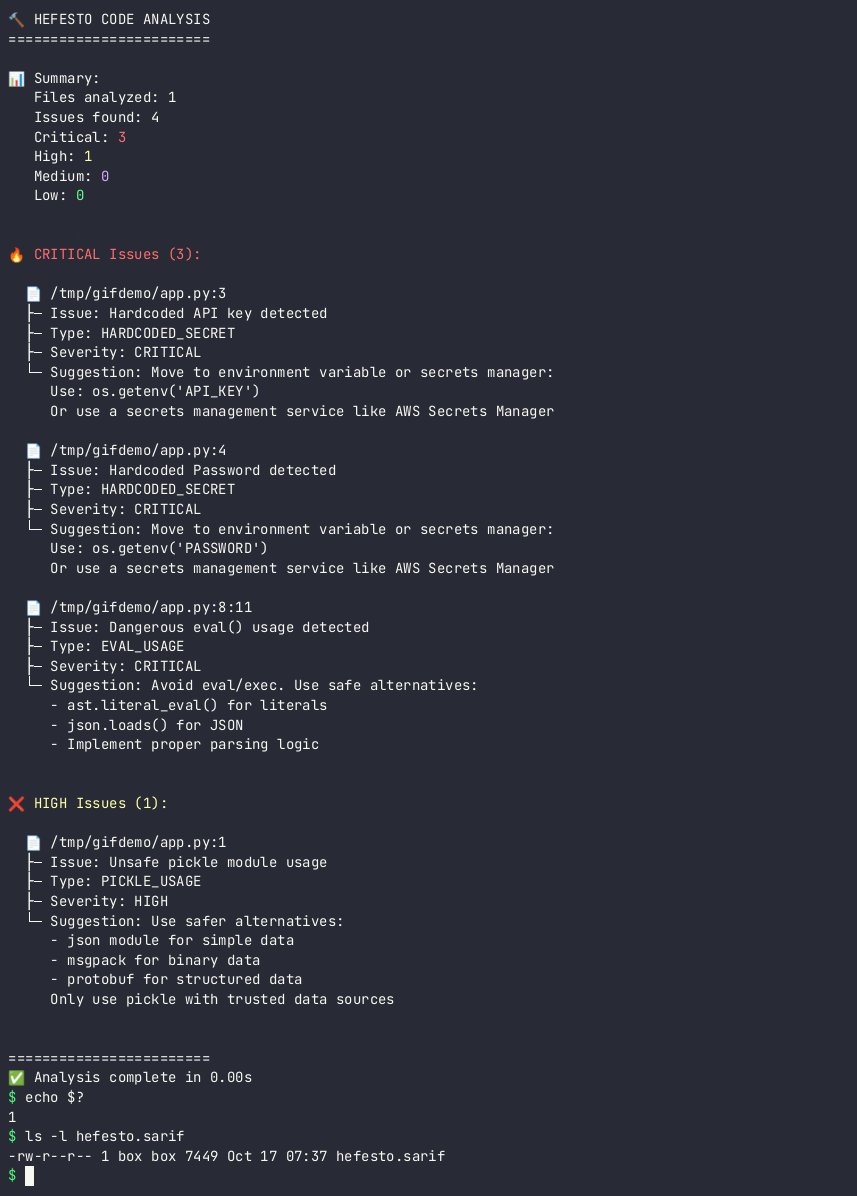
--fail-on high exits 1 when a finding at that severity or above shows up, so CI can block the merge. Results also go to a SARIF file.Try It
Recorded with hefesto-ai 4.20.1 on a test file: the run reports the findings, writes the SARIF file and exits 1.
Same check as a GitHub Action:
MCP
HefestoAI also runs as an MCP server, so Claude Code, Cursor and other MCP clients can call it. Add it with Smithery:
Or point your client at the endpoint:
Pricing
Free Resource
10 things to verify before merging AI-generated code.
No spam. Unsubscribe anytime.
The Team